Privacy with traceability
Names and contact details are stored separately from the audit log. Access and erasure requests are assessed against the audit firm’s retention obligations.
Features
Revios brings planning, procedures, documentation and reporting together in one workflow. Here is what the tool contains, and how it keeps your data secure.
Unusual amount against history for account 6300.
Proposed based on the risk assessment.
Approved by auditor · 12:41
What sets Revios apart
Names and contact details are stored separately from the audit log. Access and erasure requests are assessed against the audit firm’s retention obligations.
Revios proposes procedures, flags unusual transactions and drafts text. Every suggestion is labelled, logged and waits for the auditor's review.
Built on ISA, SAF-T and open registers. New requirements and standards become updates to the tool, not changes to how you work.
Encrypted in transit and at rest, role-based access and a signed log that shows who did what and when.
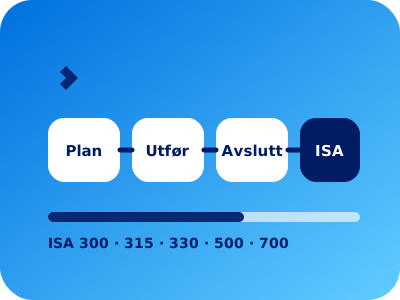
Planning, fieldwork, completion and reporting follow the phases in ISA. Procedures and documentation land where the standard expects them.
Fetch master data, roles and financials from the Brønnøysund registers and import SAF-T files straight onto the engagement.
The engagement partner, staff and quality reviewer work on the same engagement with role-based permissions. Approval happens where the work is.
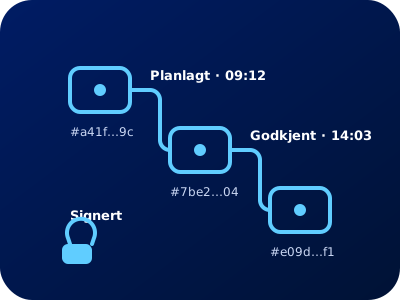
Every action is chained and signed. The log shows who did what and when, and cannot be altered afterwards.
One workflow
Review the proposed audit plan and adjust the materiality threshold.
Look up the entity by organisation number. Master data is fetched from open registers, and the risk assessment gives a proposed audit plan you can adjust.
Review the proposed audit plan and adjust the materiality threshold.
Import SAF-T, perform the procedures and gather evidence, judgements and clarifications on the engagement. Status and ownership are visible to the whole team.
Document the results of the procedures that are ready for review.
See what remains, assess the findings together and approve the work. Quality review happens on the same engagement.
Assess the findings together and approve completion of the engagement.
Finalise the report and letters based on what has been documented. Everything is traceable in the signed log.
Finalise the auditor's report and the letter to management.
AI with the auditor in the driver's seat
AI suggestions are labelled in the interface, stored with their reasoning and have no effect until an auditor approves them. Rejected suggestions are logged too.
Unusual amount against history for account 6300.
Proposed based on the risk assessment.
Approved by auditor · 12:41
Signed audit log
The log is chained and signed. It records events and pseudonymous user references, while names and document contents remain outside. User references can still be personal data, and retention obligations may limit erasure.
#a41f…9c#3d7e…b2#7be2…04#e09d…f1Norwegian data from day one
Fetch the entity, roles and financials from open registers, and import SAF-T files directly onto the engagement. Reconciliation against the general ledger happens in the same flow.
Reconciling against general ledger · 72%
The team together
The engagement partner, staff and quality reviewer see the same engagement with permissions tailored to their role. Approval happens where the work is.
Security
Security is not a setting in Revios. It is how the tool is built.
Read the privacy policyThe whole engagement lives in one workflow that follows the phases in ISA. You stop moving information between spreadsheets, folders and email, and the team always sees what is done and what remains.
We walk through the workflow with your team and show how Revios fits in.